What Is an AI Agent? How AI Agents Work
The important difference between AI that answers a question and AI that completes a task is its ability to act.
An AI agent is a software system that uses artificial intelligence to pursue a goal, decide what to do next, use available tools, take actions, observe the results and adjust its approach until it reaches a stopping point.
A chatbot primarily generates a response. An AI agent can potentially search for information, retrieve data, execute code, call APIs, operate software or coordinate other agents, then decide its next move based on what happened.
The AI model itself is only one part of the system. A useful modern agent is better understood as a complete stack of model, instructions, context, state, memory, tools, permissions, orchestration and safeguards.
This distinction matters because the term “AI agent” is now applied to systems with very different levels of capability. Some are little more than assistants with tool access. Others can independently work through long sequences of decisions and actions.
Key Takeaways
- An AI agent pursues a goal through a repeated cycle of deciding, acting, observing and adjusting rather than simply generating one response.
- The model is only one component. Tools, context, state, memory, permissions and safeguards determine what an agent can actually accomplish.
- The clearest sign of an agent is dynamic action selection: the system can decide what to do next based on what happened previously.
- RAG, chatbots and automated workflows are not automatically AI agents, although they can be components of an agentic system.
- Autonomy exists on a spectrum. An agent can independently choose how to complete a task while humans still control its goals, tools and permissions.
- Agents are most useful when the goal is clear but the exact path depends on intermediate results. Predictable processes are often better handled by simpler workflows.
What Is an AI Agent?
An AI agent is a system that can pursue an objective through a sequence of decisions and actions instead of merely producing a single response.
There is no single universally enforced industry definition. Different organizations draw the boundary differently.
Google Cloud describes AI agents as software systems that use AI to pursue goals and complete tasks on behalf of users, with capabilities that can include reasoning, planning, memory and autonomous decision-making.
Microsoft similarly describes agents as systems that can interpret information, make decisions and take actions in pursuit of objectives.
A particularly useful architectural distinction comes from Anthropic’s Building Effective Agents guidance. Anthropic distinguishes workflows, where models and tools follow predefined code paths, from agents, where the model dynamically directs its own processes and tool use.
The terminology varies, but modern definitions converge around three characteristics:
Goal: The system has an objective to accomplish.
Agency: It has some freedom to determine how to pursue that objective.
Action: It can interact with tools or an environment rather than only return text.
The last two characteristics are what separate an agent from many ordinary AI applications.
A language model can tell you how to reorganize a spreadsheet.
An agent may be able to open the data, analyze it, make the changes, check the result and return the completed file.
What Actually Makes an AI System an Agent?
“AI agent” has become a broad product label, so the name alone tells you very little.
A better approach is to examine the system’s behavior.
Use these five questions:
| Question | What a “yes” indicates |
| Does the system receive a goal rather than only generate a response? | Goal-oriented behavior |
| Can it choose its next step dynamically? | Agency |
| Can it use tools or interact with an environment? | Ability to act |
| Can it observe results and change course? | Feedback-driven behavior |
| Can it execute multiple actions without new human instructions between every step? | Meaningful operational autonomy |
A system does not necessarily need every possible capability to qualify as an agent.
The most useful dividing line is this:
An AI system becomes meaningfully agentic when it can repeatedly choose and execute actions based on what happens during the task.
That distinction is more useful than asking whether the product has a chat interface or uses a particular model.
Agent or not?
Consider several common AI systems.
| System behavior | Agent? | Why |
| Generates an email from one prompt | Usually no | Produces a model response |
| Searches a fixed document index and answers | Not necessarily | Could be predetermined RAG |
| Executes a fixed five-step automation | Usually a workflow | Path is defined beforehand |
| Chooses whether to search, query an API or ask the user | Yes | Dynamically selects actions |
| Diagnoses a problem, tries tools, observes failures and retries | Yes | Uses an agentic feedback loop |
| Executes a predefined script | No | No dynamic decision-making |
This also explains why adding an LLM to an application does not automatically make the application an AI agent.
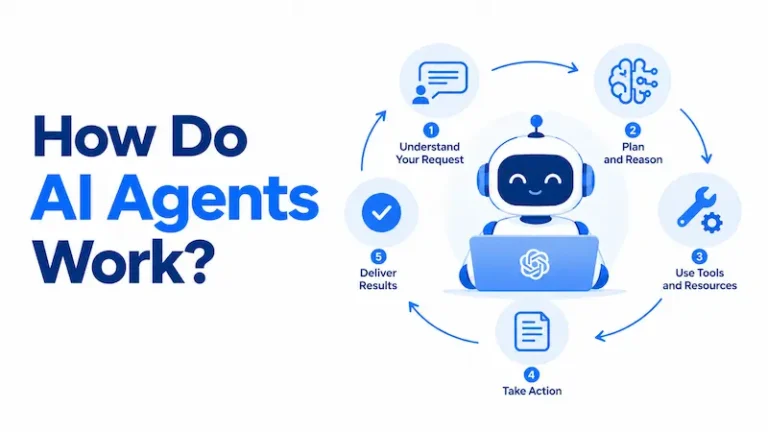
How Do AI Agents Work?
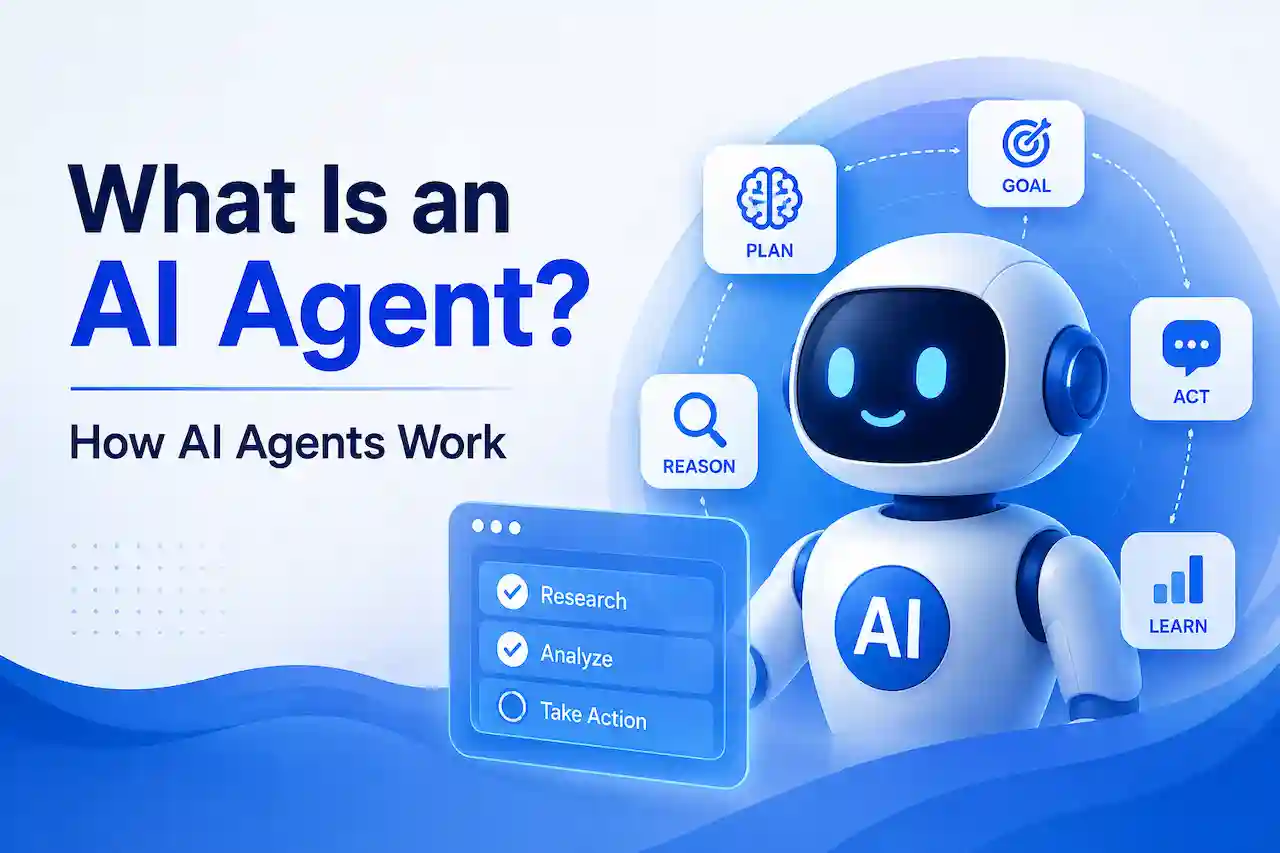
Modern AI agents generally operate through a feedback loop.
A simplified version is:
Goal → Context → Decide → Act → Observe → Update → Repeat or Stop
The exact implementation differs between systems, but the underlying pattern is consistent.
1. The agent receives a goal
Every agent needs an objective.
A user might ask:
Compare three suppliers and identify which offers the best terms.
A software system might trigger:
Investigate this failed deployment.
Or an event might initiate:
Process this new customer-support request.
The goal defines what success should look like.
Humans or developers typically also establish system instructions defining how the agent should behave, what resources it may use and which actions require approval.
2. The agent receives relevant context
The model needs information before it can make a useful decision.
That context might include the user’s request, documents, application data, database records, conversation history, tool descriptions or results from previous actions.
The important point is that context can change throughout the task.
If an agent searches a database and finds three relevant records, those results can become context for the next decision.
3. The model determines the next action
The model evaluates the information currently available and selects an appropriate next step.
It may determine that it should:
- retrieve more information
- use a particular tool
- inspect a file
- execute code
- delegate work
- ask for clarification
- request human approval
- finish the task
Some agent systems generate explicit plans. Others choose one action at a time.
The defining feature is that every future step does not necessarily need to be predetermined by the developer.
4. The agent uses a tool
Tools connect model decisions to external capabilities.
An agent might be able to search the web, retrieve company documents, query databases, call APIs, execute code, inspect files or interact with software.
The model itself usually does not directly perform all these external operations.
Instead, a typical tool-calling process works like this:
Developer exposes available tools → model selects a tool → model produces structured arguments → application executes the tool → result returns to the model → model decides what happens next
This distinction matters.
The model decides what it wants to do. The surrounding software gives that decision operational effect.
5. The agent observes the result
Every action produces information.
A search returns documents.
A database query returns records.
Code may run successfully or produce an error.
An API may reject a request.
A browser action may reveal an unexpected page.
That result becomes a new observation.
6. The agent adjusts its approach
The agent can then decide whether the previous action worked.
It might conclude:
The search did not find an authoritative source. I should change the query.
Or:
The test failed because a dependency is missing. I should inspect the configuration.
Or:
The objective has been completed.
This feedback is what turns a sequence of AI calls into an agentic loop.
7. The agent stops or escalates
Agents need stopping conditions.
Execution may stop because the objective has been achieved, a maximum number of steps has been reached, a policy blocks the next action, a tool has failed repeatedly or human authorization is required.
A well-designed agent therefore needs to determine not only what to do next, but also when it should not continue autonomously.
Example: How an AI Research Agent Completes a Task
Consider this goal:
Compare the current AI risk-management guidance from three authoritative organizations.
A research agent might work through the task like this.
Step 1: Interpret the objective
The model determines that the task requires current primary sources, comparable information and a final synthesis.
Step 2: Decide what information is needed
It identifies relevant organizations and decides that official documentation should take priority over secondary articles.
Step 3: Use a search tool
The agent submits searches and receives candidate sources.
Step 4: Evaluate the results
It rejects irrelevant or outdated pages and opens stronger primary sources.
Step 5: Extract information
The agent retrieves the sections needed for comparison and maintains the findings in its current task state.
Step 6: Detect missing information
If one source does not answer an important comparison question, the agent can search again rather than blindly continuing.
Step 7: Synthesize
It organizes the evidence into common themes, differences and practical implications.
Step 8: Verify
The agent checks whether important claims are actually supported by the retrieved sources.
Step 9: Stop
Once the comparison meets the defined objective, it returns the result.
The important point is not the research topic.
It is what happens between the user’s instruction and the final answer.
The agent repeatedly makes decisions based on new information instead of following one completely predetermined path.
The AI Agent Stack: What Components Make an Agent Work?
Calling an agent “an LLM with tools” is useful shorthand, but it leaves out much of what determines whether an agent works reliably.
A more complete model is the AI Agent Stack:
| Layer | Key question |
| Goal and instructions | What should the agent accomplish? |
| Model | What interprets information and selects actions? |
| Context | What information can the model see right now? |
| State | What has happened during the current task? |
| Memory | What information can be retained and retrieved later? |
| Tools | What can the agent actually do? |
| Permissions | Which resources and actions are allowed? |
| Orchestration | How are actions, loops and handoffs coordinated? |
| Runtime | Where does execution happen? |
| Guardrails | What constrains unsafe or inappropriate behavior? |
| Evaluation and observability | How do operators know whether the agent works correctly? |
This leads to one of the most important principles for understanding AI agents:
An agent’s real capability is determined by the whole system, not by the model name alone.
Two agents using the same underlying model may have radically different capabilities because one can search the web and execute code while the other cannot access anything beyond its prompt.
Model: the decision engine
The model interprets instructions and information and determines possible next actions.
Modern agents often use large language models because LLMs can work with natural language, code, structured tool calls and diverse information.
But AI agents are older than LLMs. Planning systems, rule-based agents and reinforcement-learning agents can also fit broader definitions of agency.
The current wave of AI agents is distinctive because generative models make flexible interaction with tools and complex instructions substantially easier.
Tools: how the agent acts
Tools transform model output into operational capability.
Without a tool, a model might explain how to check a calendar.
With calendar access, an agent may be able to check it.
Without code execution, a model can generate a program.
With an execution environment, an agent can run that program, observe an error, modify the code and try again.
Tools are where model decisions become external actions.
Context: what the model can see now
Context is the information currently available to the model during a decision.
It may contain:
- instructions
- conversation history
- retrieved documents
- tool descriptions
- recent tool results
- task information
Context is temporary from the perspective of an individual model call. Agent systems must decide which information should be included when another decision is required.
State: what has happened during the task
State tracks the progress of the current execution.
For example:
Search completed → three sources retrieved → source two rejected → comparison still missing pricing information.
That is not exactly the same thing as context or long-term memory.
State represents where the agent currently is in the task.
Memory: what can be retained and retrieved
“Memory” is frequently misunderstood.
In many AI agent architectures, memory is engineered outside the underlying model.
Information might be stored in:
- conversation state
- databases
- files
- vector stores
- knowledge systems
- structured user profiles
The system retrieves relevant information later and supplies it to the model as context.
Agent memory therefore should not be interpreted as unlimited human-like recall inside the AI model.
A useful distinction is:
| Concept | Meaning |
| Context | What the model can access during the current decision |
| State | What has happened during the current task |
| Memory | Information stored for retrieval across steps or sessions |
Keeping these concepts separate makes modern agent architecture much easier to understand.
Orchestration: how the system coordinates work
Orchestration manages execution around the model.
It may control when tools run, how results return, when an agent loops, when tasks execute in parallel, when another agent receives work and when human approval is required.
OpenAI’s current agent tooling includes orchestration capabilities such as handoffs, guardrails and tracing for this reason.
Runtime: where actions happen
Agents that execute work need an environment in which that work can happen.
A coding agent, for example, might require a filesystem, command line, installed dependencies, sandbox, temporary storage and controlled network access.
The runtime therefore determines part of what the agent can actually accomplish.
Identity and permissions: what the agent is allowed to do
Once an agent connects to real business systems, authorization becomes critical.
An agent might technically know how to update a database, but whether it can do so should depend on its permissions.
The U.S. National Institute of Standards and Technology has highlighted this issue through its work on software and AI agent identity and authorization, reflecting the growing need to control how non-human actors authenticate and what resources they can access.
Permissions are therefore part of agent capability, not merely a security setting added later.
Guardrails: where autonomy stops
Autonomy does not require unlimited freedom.
An organization might allow an agent to read a calendar and prepare an invitation automatically but require human approval before sending it.
The system remains agentic. Its autonomy is simply bounded.
For higher-impact applications, this boundary becomes fundamental to safe deployment.
AI Agent vs LLM: What Is the Difference?
An LLM and an AI agent are not the same thing.
A large language model generates predictions based on its input. An AI agent is a larger system that may use an LLM as its decision engine while adding tools, context, state, memory and an action loop.
A useful analogy is:
LLM = engine
AI agent = vehicle built around the engine
The engine contributes much of the capability, but the vehicle determines where it can go, what it can carry and what controls are available.
An LLM can therefore be part of an agent without being an agent by itself.
AI Agent vs Chatbot: What Is the Difference?
A chatbot’s primary role is conversation.
You might ask:
What should a weekly project report contain?
The chatbot generates an answer.
An agent could potentially retrieve project records, identify overdue tasks, calculate progress and prepare the report itself.
The distinction is not the interface.
An AI agent can still communicate through a chat window.
What matters is whether the system behind that interface can choose and execute actions toward an objective.
AI Agent vs AI Assistant
“Assistant” describes a product role rather than a precise technical architecture.
Some AI assistants primarily respond to prompts.
Others have substantial agentic capabilities.
Instead of relying on the product label, ask:
Can this system independently choose and execute multiple actions toward my objective?
If it can, the assistant is exhibiting agentic behavior.
AI Agent vs Automated Workflow
This is one of the most important distinctions.
A workflow could look like:
New invoice → extract fields → check amount → route for approval
The developer determines the path.
An agent might instead receive:
Investigate why this invoice cannot be processed and resolve the issue if possible.
It could inspect the invoice, query supplier records, identify missing information and decide which system to use next.
Anthropic’s Building Effective Agents guidance makes this distinction explicit: workflows follow predefined code paths, while agents dynamically direct their own processes and tool use.
A useful rule is:
Use a workflow when the path is known. Use an agent when the path must be discovered.
AI Agent vs RAG: What Is the Difference?
Retrieval-augmented generation, or RAG, and AI agents solve different problems.
RAG gives a model access to relevant external information, often by retrieving documents before generating an answer.
An agent can use retrieval too, but it can also decide whether retrieval is necessary and what should happen afterward.
| RAG application | AI agent |
| Primarily retrieves information to improve an answer | Pursues a broader task objective |
| Retrieval process may be predetermined | Can dynamically choose tools and actions |
| Often centered on answering | Often centered on task completion |
| May use one retrieval-response cycle | May execute many action-observation cycles |
| Does not inherently require agency | May use RAG as one of several tools |
Microsoft’s current guidance on AI agent adoption similarly distinguishes conventional retrieval patterns from systems that dynamically determine which knowledge sources and tools to use.
RAG can therefore be part of an AI agent without being an AI agent itself.
AI Agent vs Agentic AI
The terms are related but not perfectly interchangeable.
An AI agent usually refers to an individual software system capable of pursuing goals and taking actions.
Agentic AI describes the broader approach of designing AI systems around agency, autonomous decision-making and action.
An agentic system could contain:
- one agent
- several specialized agents
- fixed workflows
- retrieval systems
- tools
- memory
- human approval stages
A useful shorthand is:
AI agent = an acting unit
Agentic AI = the broader system or design approach built around AI-driven agency
What Are Multi-Agent Systems?
A multi-agent system uses several agents rather than asking one agent to perform every responsibility.
For example, a system could contain a research agent, coding agent and verification agent coordinated by another component.
Agents may work sequentially, in parallel or through handoffs.
Multi-agent architecture can make specialization useful for genuinely complex tasks, but it also introduces coordination overhead, additional model calls, more state to manage and more possible failure points.
More agents do not automatically make a system more intelligent or reliable.
What Types of AI Agents Exist?
There are two useful ways to classify AI agents.
Traditional AI literature classifies them according to how they make decisions.
Modern applications are often easier to understand according to what they do.
Classical AI agent types
| Type | Basic behavior |
| Simple reflex agent | Responds to current conditions using defined rules |
| Model-based agent | Maintains a representation of its environment |
| Goal-based agent | Selects actions based on desired outcomes |
| Utility-based agent | Compares actions according to expected value or preference |
| Learning agent | Improves behavior using experience or data |
These categories remain conceptually useful, but a modern LLM-based agent may combine characteristics from several of them.
Modern functional agent types
Modern agent applications are often described by function instead.
A research agent searches, retrieves, analyzes and synthesizes information.
A coding agent reads, writes, executes and tests software.
A computer-use agent interacts with graphical interfaces or websites.
A customer-service agent works with customer information, knowledge bases and business systems.
A data agent queries, transforms or analyzes organizational data.
A specialist agent focuses on a specific technical or business domain.
A multi-agent system coordinates several agents to solve different parts of a larger task.
These categories overlap. A research agent may use code, while a coding agent may search technical documentation.
How Autonomous Are AI Agents?
Autonomy is not binary.
An agent can have freedom over how it completes a task while humans continue controlling what task it receives and what resources it may access.
| Autonomy level | Example |
| Low | Chooses which information source to search |
| Moderate | Executes several steps but requests approval for consequential actions |
| High | Completes long multi-step tasks with limited intervention |
| Very high | Plans and performs consequential work within broad predefined permissions |
Humans may still define:
- objectives
- system instructions
- available tools
- credentials
- permissions
- resource limits
- approval boundaries
- stopping conditions
An agent therefore does not need independent goals or unrestricted control to be meaningfully autonomous.
What Can AI Agents Do?
Agent capabilities depend heavily on the model, tools and permissions available.
Research
An agent can search multiple information sources, retrieve relevant material, compare evidence and produce a synthesized result.
Software development
A coding agent can inspect repositories, modify files, execute tests, analyze failures and revise its implementation.
Customer support
Within appropriate permissions, an agent can retrieve account information, consult company policies and determine what next action is appropriate.
IT operations
An agent may investigate alerts, examine logs, query monitoring systems and recommend or execute predefined remediation.
Data analysis
An agent can retrieve datasets, run calculations, generate code, inspect results and adapt its analysis.
Administrative work
Agents can potentially coordinate information across calendars, documents, communications and other applications.
The common characteristic is not the industry.
It is:
goal → decisions → actions → observations → adjustment
When Should You Use an AI Agent?
Not every AI problem needs an agent.
In fact, choosing an agent when simpler software would work can make a system slower, more expensive and harder to evaluate.
Anthropic’s engineering guidance recommends starting with the simplest solution that meets the requirement and introducing agentic complexity only when it produces enough value to justify the additional cost and latency.
A useful decision framework is:
| Situation | Better starting point |
| One answer or transformation is needed | Single model call |
| External knowledge must be retrieved | Model + RAG |
| Steps are known and predictable | Workflow |
| Path depends on intermediate results | Agent |
| Distinct specialties genuinely need coordination | Possibly multi-agent |
Agents make the most sense when three conditions overlap:
The objective is clear.
The exact path cannot be completely predetermined.
The system can safely receive enough autonomy to discover that path.
When Should You Not Use an AI Agent?
Agentic architecture should not be the default simply because it is technically possible.
A deterministic workflow may be better when the steps are known, repeatability is critical or flexibility adds little value.
For example, if every invoice must always pass through the same six validation rules in the same order, traditional software or a fixed workflow may be simpler and easier to audit.
Agents can also be a poor choice when:
Consistency matters more than flexibility.
A deterministic system may produce more predictable outcomes.
Latency is critical.
Agent loops can require many model calls and tool interactions.
The task is extremely simple.
One model call may accomplish the same result.
The action is highly consequential.
If mistakes could create serious financial, safety, legal or security consequences, autonomy may need to be heavily constrained.
The process must be completely reproducible.
Agents may choose different valid or invalid paths across separate runs.
A mature AI strategy therefore asks not only:
Where can we use agents?
but also:
Where would an agent introduce unnecessary uncertainty?
Why Are AI Agents Useful?
Agents are valuable because many real tasks cannot be completed with one model response.
They reduce repeated prompting
Instead of requiring a user to manually direct every next step, an agent can manage part of the sequence itself.
They adapt to intermediate results
Traditional automation works well when the path is predetermined.
Agents become useful when the correct next step depends on what happened previously.
They connect reasoning with software
Tools allow the model’s decisions to affect external applications and data.
They can handle longer tasks
Agent loops make it possible to work through problems requiring multiple searches, calculations, edits or tool interactions.
The same characteristics that make agents useful, however, also make them harder to control.
What Are the Limitations of AI Agents?
Agents inherit the weaknesses of their underlying AI models while adding new failure modes created by multi-step execution.
Errors can compound
A wrong answer from a chatbot may affect one response.
A wrong decision early in an agent task can influence every later action.
For example, if a research agent incorrectly classifies an unreliable source as authoritative, later analysis may build on that mistake.
Longer task chains therefore create more opportunities for errors to propagate.
Agents can choose poor actions
An agent may misunderstand the objective, choose the wrong tool or continue pursuing an unproductive approach.
Context becomes harder to manage
Long tasks can generate more information than should remain available to the model at every step.
Agent systems need mechanisms for retrieving, summarizing and discarding information appropriately.
External tools fail
An agent can make a sensible decision and still encounter an unavailable API, expired credential, changed interface or permission error.
Reliable agent design therefore involves the surrounding software environment as much as the model.
Agents can cost more
A single response may require one model invocation.
A long-running agent can require many model calls, searches and external operations.
Flexibility therefore comes with computational and operational cost.
Evaluation is more difficult
A fixed workflow follows a predictable path.
An agent may reach the same objective through different sequences of actions, which makes testing and debugging harder.
What Are the Main AI Agent Security Risks?
The security impact of an AI agent depends heavily on what the agent can access.
A text-only agent with no external tools has a very different risk profile from an agent that can modify production systems.
Excessive permissions
Giving agents unnecessary credentials increases the consequences of mistakes or compromise.
Least privilege should apply to AI agents just as it applies to human and machine identities.
Prompt injection
Agents may consume instructions and data from websites, documents, messages and external systems.
Malicious content can attempt to manipulate an agent into following instructions that conflict with its intended task.
This becomes particularly consequential when the agent has powerful tools.
Sensitive-data exposure
An agent with access to private information could accidentally send that information through an inappropriate external service or tool.
Unintended actions
The system may pursue the stated goal in a way the user did not expect.
Approval gates are therefore valuable when actions are difficult to reverse or carry significant consequences.
Weak accountability
Organizations need to know which agent performed an action, which identity it used, which tools were called and whether a human authorized consequential steps.
That makes identity, logging and tracing important components of agent governance.
How Can Organizations Use AI Agents More Safely?
Agent security should be designed around capability and consequence, not only model quality.
Apply least privilege
Give an agent access only to the resources required for its function.
A research agent that only needs to read documents should not have permission to delete them.
Separate information access from consequential actions
Reading a record and permanently changing it should not automatically receive the same level of autonomy.
Use human approval where the consequences justify it.
Use attributable agent identities
Where possible, agents should act through identifiable machine identities rather than shared privileged human accounts.
Treat tools as security boundaries
Text instructions alone should not be relied on to prevent actions that must never occur.
If an agent should not be able to perform an operation, restrict the underlying permission or tool.
Monitor execution
Logs and traces help operators understand which actions agents selected and what happened afterward.
Evaluate complete tasks
Testing should examine whether the full agent completes the right objective, uses appropriate tools, respects boundaries and handles failure safely.
A model that performs well on isolated prompts does not automatically produce a reliable agent.
What AI Agents Are Not
Understanding the boundaries of the term helps prevent several common misconceptions.
An AI agent is not necessarily a robot. Most agents are software systems.
An AI agent is not automatically conscious. Software agency describes goal-directed decision and action, not consciousness or self-awareness.
An AI agent is not simply an LLM. The model may be the decision engine, but the surrounding system provides the tools and environment needed to act.
An AI agent does not require unlimited autonomy. Human approvals and restricted permissions can be part of a well-designed agent.
More agents are not automatically better. Multi-agent architectures can introduce additional coordination, cost and failure modes.
Conclusion: An AI Agent Turns AI From a Responder Into an Actor
An AI agent is best understood as a system that uses AI to decide and act in pursuit of a goal.
The defining feature is not a particular model, interface or product label.
It is the feedback loop:
goal → decide → act → observe → adjust
That loop allows an AI system to move beyond producing suggestions and begin carrying work toward completion.
But the model is only one layer.
The real capability of an AI agent comes from the complete AI Agent Stack: the model it uses, the context it receives, the state it maintains, the memory it can retrieve, the tools it can operate, the permissions it holds and the safeguards controlling its behavior.
That leads to a practical way to evaluate any product marketed as an AI agent:
Can the system dynamically choose what to do next, take an action, observe what happened and adjust without a human directing every individual step?
If it can, it is meaningfully agentic.
The next question is not whether greater autonomy is technically possible. It is whether the task actually benefits from it.
For predictable work, a simple model call, RAG system or deterministic workflow may be better. For tasks where the goal is clear but the path must be discovered, an AI agent can provide something fundamentally different: the ability to decide what comes next.